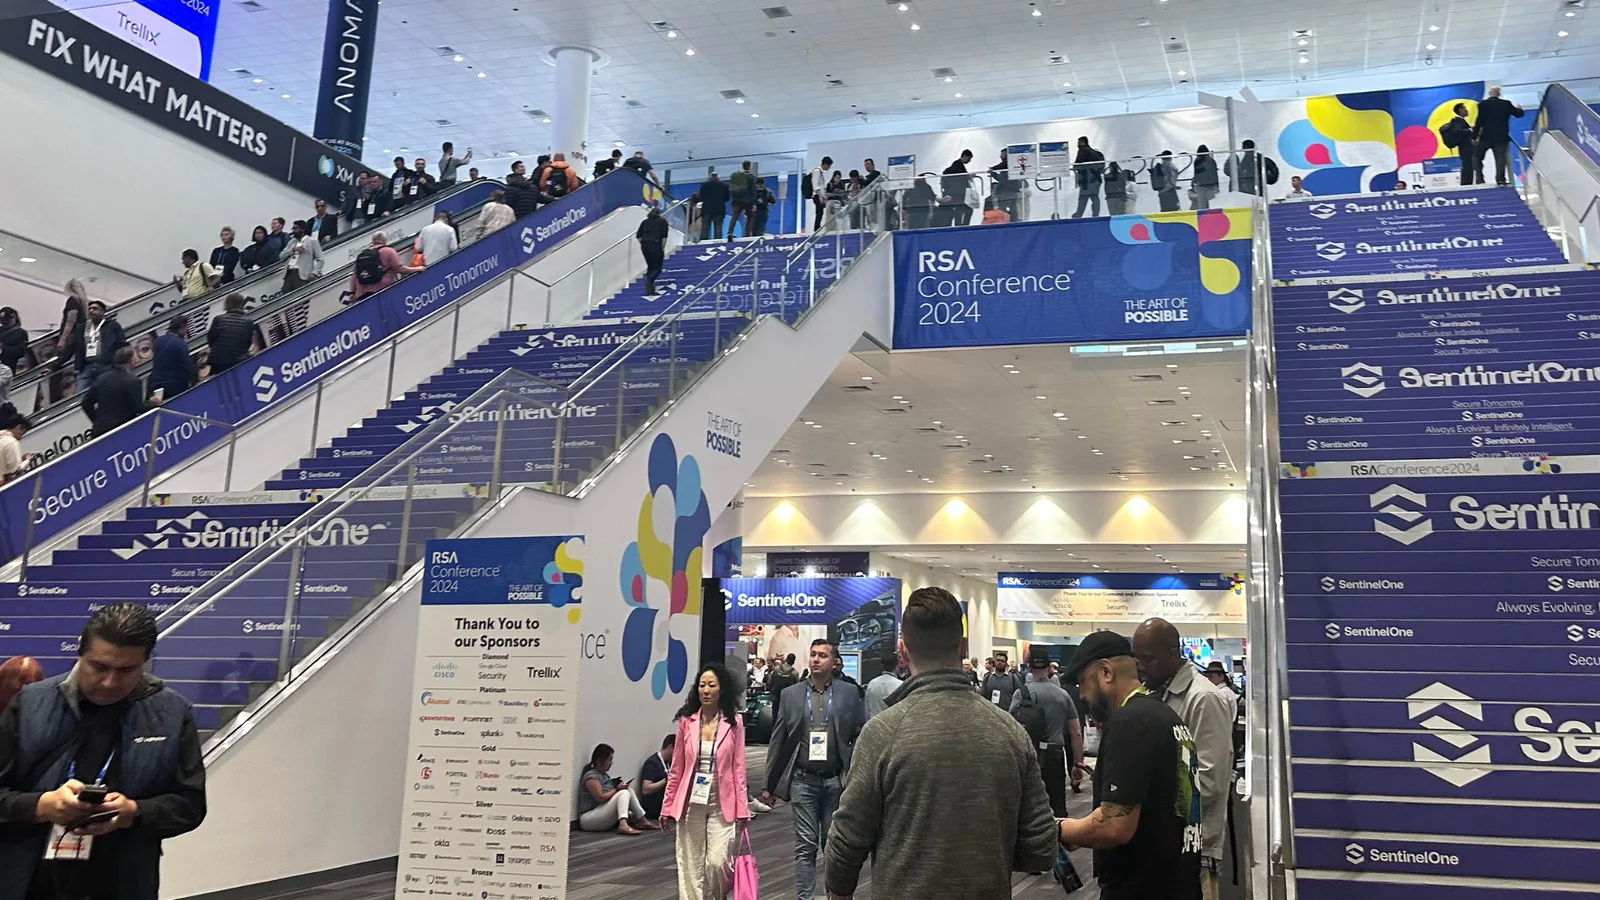
RSA Conference 2027 runs April 5–8 in San Francisco, and AI remains the dominant topic shaping the cybersecurity industry's agenda. Here's what to know heading in, based on where the conversation has been trending.
AI is a double-edged sword in cybersecurity
AI's dual role in cybersecurity has been a major recent theme. Malicious actors are leveraging AI to develop more sophisticated attacks, from AI-driven phishing campaigns to malware that adapts and evades traditional defenses. At the same time, AI offers powerful tools to enhance security, including AI-powered threat detection and automated response protocols. The takeaway holds: AI can be a formidable adversary and an invaluable ally at once.
AI is reshaping the cybersecurity workforce
AI's role in the job market remains a critical discussion point. It's both a job generator and a job replacer: it automates routine tasks, which can reduce demand for certain roles, while creating new ones that require a workforce skilled in both AI technology and cybersecurity fundamentals. Given the ongoing shortage of cybersecurity talent, this trend points to continuous learning and adaptation as a baseline requirement, not a nice-to-have.
The gap between AI hype and practical application
Despite the buzz, there's been a noticeable gap between AI's theoretical potential and its current practical application in cybersecurity. Sessions have tended to highlight future capabilities more than concrete real-world examples of AI making a significant impact one way or the other. That gap is worth watching closely at the 2027 edition, since it signals how much of the AI security narrative is still ahead of the tooling.
What to watch for at RSA 2027
Recent editions have introduced AI-powered security coworkers for triaging user-reported threats, risk management tools for AI model data and access, AI exposure management for identifying vulnerabilities in AI infrastructure, and monitoring tools for the hardware used to train generative AI models. Expect the 2027 edition to push further into securing AI systems themselves, not just using AI to secure everything else.